We harden your infrastructure to make it resilient against attacks and ransomware.
We close backdoors, harden Linux and Windows operating systems, deploy next-gen WAFs, and secure Docker containers and CI/CD pipelines. We bring your systems up to high defense-in-depth standards.
What we deliver
Who is this for? Businesses and system administrators needing to secure production servers, protect sensitive databases from data leaks, and ensure misconfigurations never compromise operations.
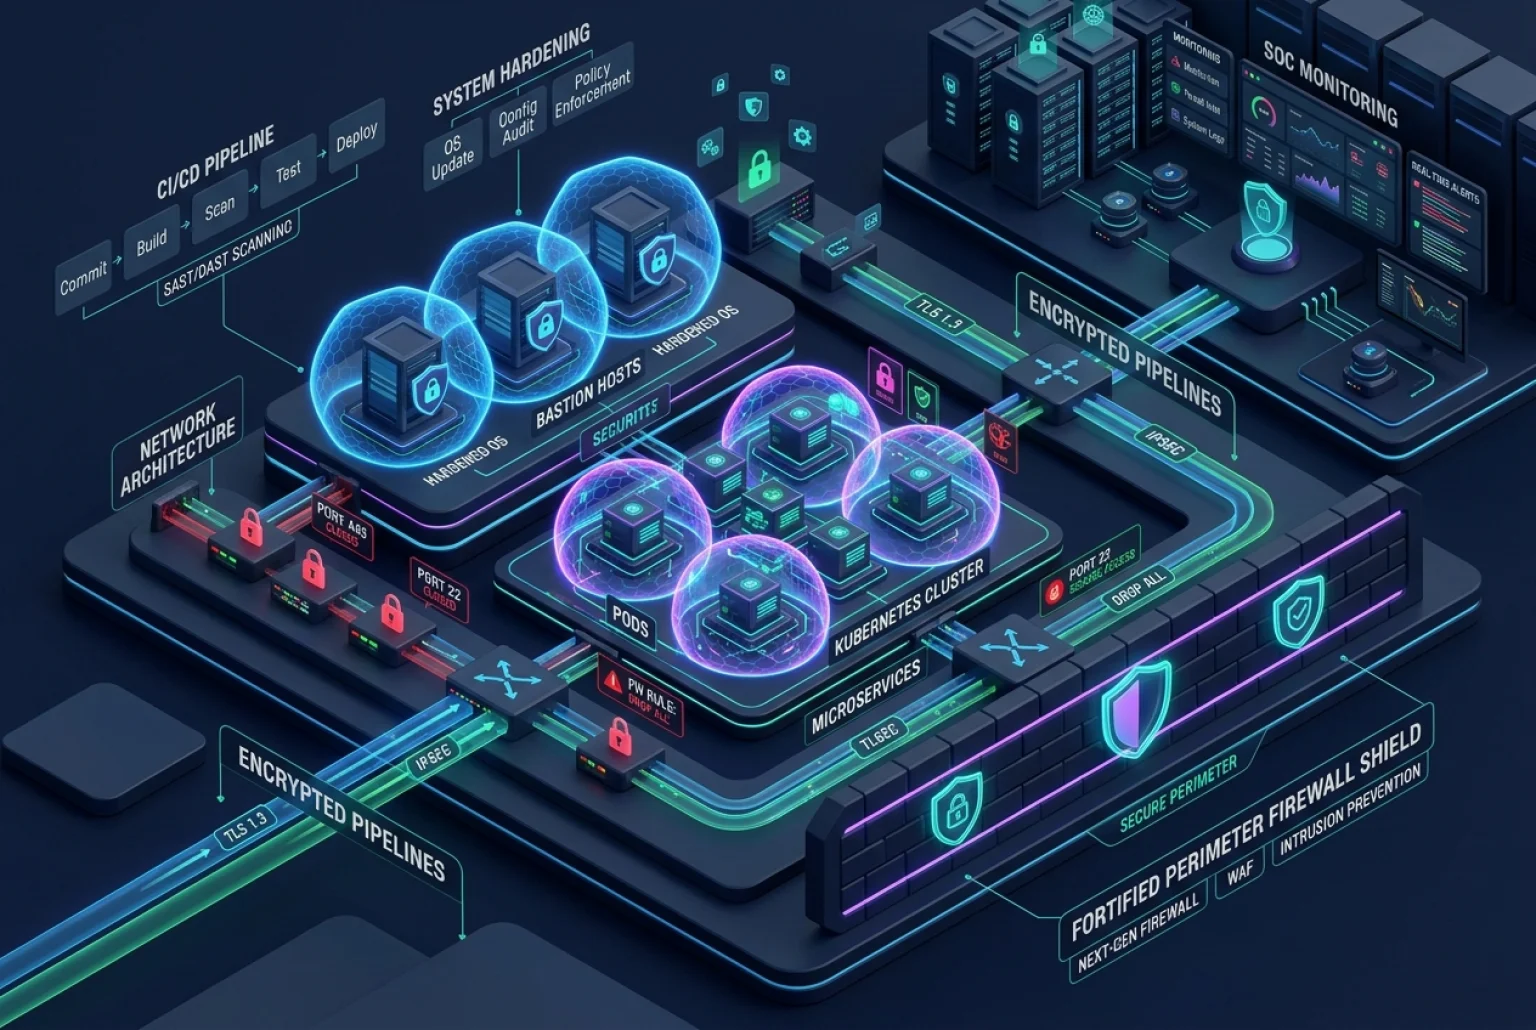
- Server Hardening (Linux / Windows): Applying CIS Benchmarks, disabling redundant services, enforcing cryptographic SSH key authentication, and tightening account policies.
- Advanced Firewalls & Perimeter Defense: Strict rule definition on UFW, iptables/nftables, and Cloudflare WAF integration to deflect DDoS and automated bot assaults.
- Docker & Container Hardening: Rootless execution, resource containment via cgroups/namespaces, container image vulnerability scanning, and isolated internal bridge networks.
- DevSecOps & Secure CI/CD Pipelines: Automated SAST code scanning, secret leak prevention, and artifact signing integrated directly into deployment workflows.
- Intrusion Detection & Active Alerting: Deployment of Fail2ban, Wazuh / OSSEC, critical file integrity monitoring, and real-time alerts upon suspicious behavior.
Concrete deliverables
Every project results in tangible deliverables that you can use, integrate, and maintain.
Reproducible playbooks and documented automation scripts to enforce identical hardening across future environments.
Tailored perimeter rules shielding infrastructure from brute-force attempts, layer-7 attacks, and malicious probes.
Active monitoring of unauthorized access attempts, privilege escalations, and automated instant notifications.
Comprehensive technical report detailing all modified parameters, closed ports, secured services, and compliance scores.
Frequent use cases where we solve your needs
Secure VPS or dedicated servers by closing redundant ports and enforcing key-based SSH authentication.
Deploying tailored WAF rules against aggressive scrapers, botnets, and resource exhaustion attacks.
Container isolation, rootless execution, and internal network segmentation preventing lateral movement.
Tools we use
How we work
Baseline & Exposure Audit
Inspection of operating system settings, active services, listening ports, and file system permissions.
Hardening Matrix Design
Definition of CIS Benchmarks baseline, firewall rules, and isolation architecture tailored to your stack.
Zero-Downtime Implementation
Staged deployment of security controls verified on staging prior to production with zero service downtime.
Stress Validation & Handover
Defensive validation of newly enforced rules, transfer of automation scripts, and technical knowledge sharing.
Frequently asked questions
Will hardening cause downtime or disruptions to my service?
Do you support any cloud provider or dedicated bare-metal servers?
How can we measure that the system is genuinely more secure?
Can we continue deploying updates to our software afterwards?
Other available services
Applications and platforms built to adapt to your processes, needs and goals.
Corporate websites, ecommerce stores, and fast, maintainable web applications built to scale.
SaaS products from early MVPs to mature platforms, scalable and ready to evolve.
Shall we start?
Tell us what you need. We analyze your requirements and coordinate the next steps with a tailored proposal.